Product overview
36 detection engines. 5-minute scans. Plain-English alerts.
SentinelSMB watches your Microsoft 365, Google Workspace, AWS, and Cloudflare accounts 24/7. Every alert explains what happened, how serious it is, and exactly what to do next — no jargon, no guesswork, no retainer.
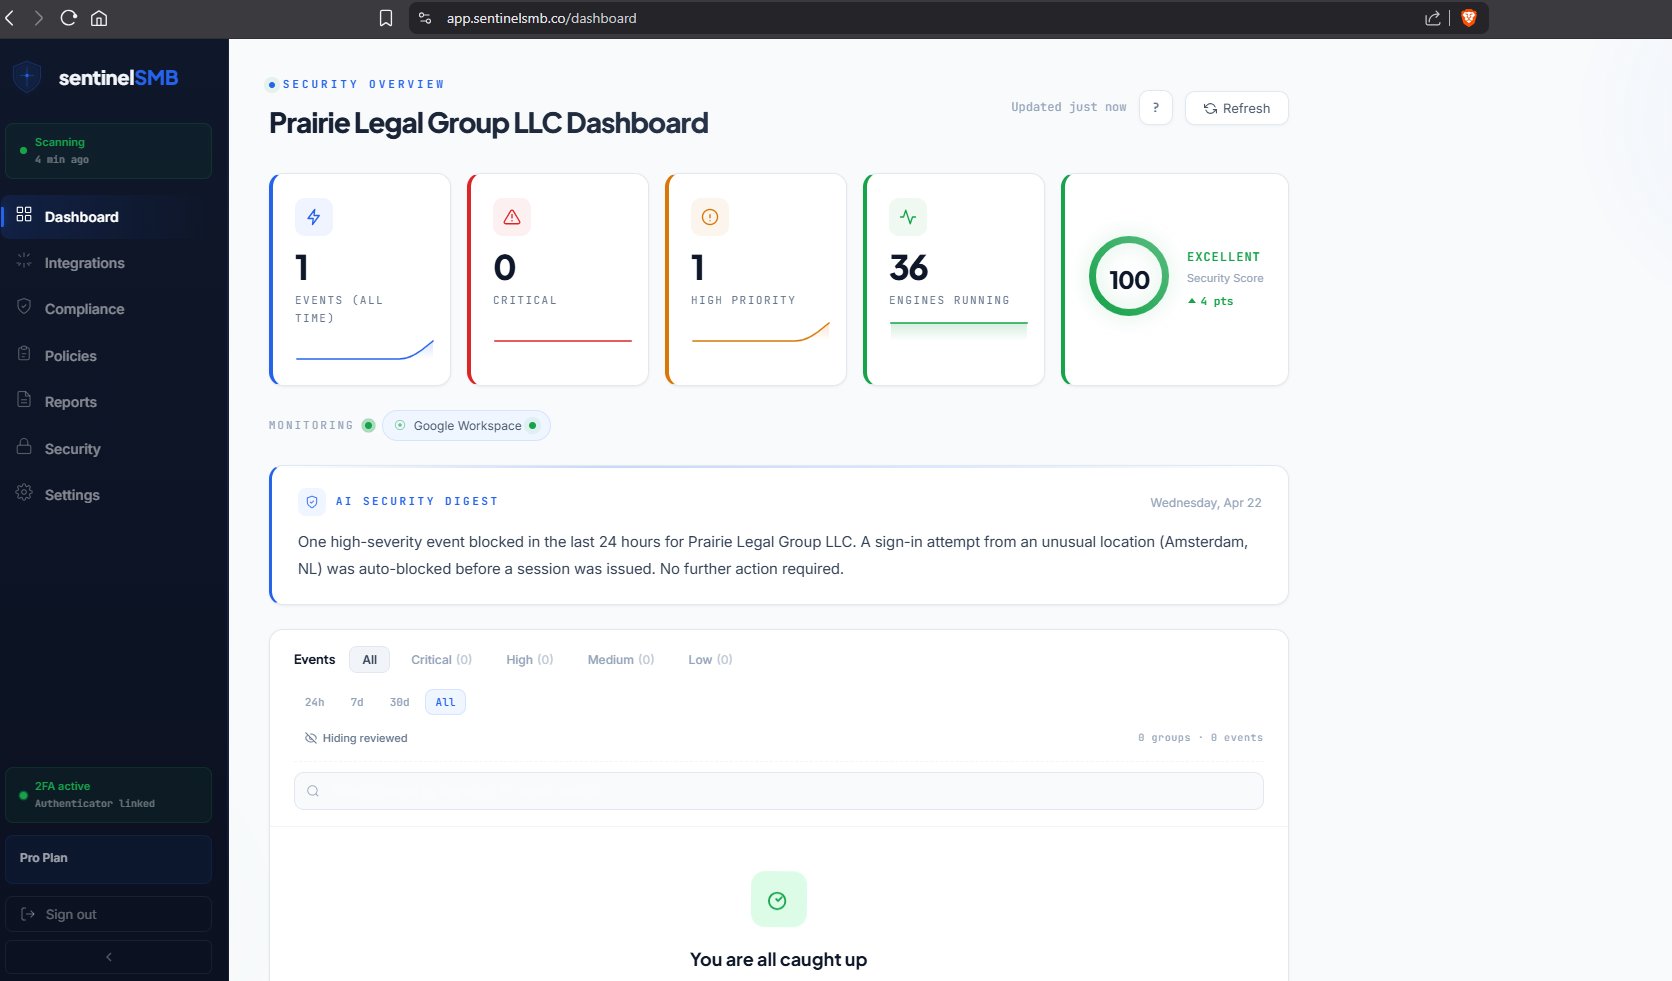
See it in action
Your security posture, live. Not once a quarter.
Every five minutes, 288 times a day, our engines sweep your accounts, cloud, and email. Critical threats surface instantly. Normal activity gets filed away.
An alert you can act on
Plain-English alert with severity, evidence, and step-by-step guidance via SMS, email, Slack, or Teams.
One score you can track
A continuous 0-100 score measuring your overall cloud security health. Track it week over week. Show it to your board, insurer, or partners.
Only what matters
Every detection is scored for severity and checked against known attack patterns, so you only see what actually matters.
How it works
From consent to answered alert in minutes.
No agent to install. No firewall to reconfigure. Connect once, and monitoring runs around the clock.
Integrations monitored
- Microsoft 365
- Google Workspace
- AWS
- Cloudflare
36
detection engines
Every 5 minutes, 288 times a day, around the clock.
Triage scores every detection for severity before anyone sees it.
Alert channels supported
- SMS
- Slack
- Microsoft Teams
-
1
Connect
You approve read-only access to Microsoft 365 or Google Workspace with one click. AWS and Cloudflare connect the same way: read-only, and we never hold your passwords or keys.
-
2
Baseline
We learn your normal activity patterns — sign-in locations, devices, work hours.
-
3
Scan
36 engines sweep your accounts every 5 minutes, 288 times a day, around the clock.
-
4
Triage
Every detection is scored for severity and checked against known attack patterns, so you only see what actually matters.
-
5
Alert & Respond
Plain-English alert with severity, evidence, and step-by-step guidance via SMS, email, Slack, or Teams.
36 engines · 7 categories
Every class of attack that hits small business, covered.
Each engine is purpose-built for a specific attack pattern we have seen hit SMBs repeatedly. Nothing generic, nothing noisy.
-
7 engines
Identity
Impossible travel, password spray, MFA bypass and fatigue, MFA gaps, stale accounts, session-token theft, account-takeover sequences.
-
2 engines
Data
Bulk downloads, anomalous file access, sensitive content exfiltration across OneDrive, SharePoint, and Google Drive.
-
3 engines
Email
Business email compromise, phishing infrastructure, and silent forwarding or inbox rule changes on the mailbox itself.
-
4 engines
Cloud
Conditional access gaps, tenant configuration drift, shadow IT and unsanctioned apps, and admin privilege escalation.
-
3 engines
Network
DNS tampering, SSL certificate changes, typosquat-domain registration targeting your brand.
-
3 engines
Threat Intelligence
URLhaus authoritative feed, HaveIBeenPwned credential exposure, AlienVault OTX threat-actor attribution.
-
14 engines
Core Platform
IP threat enrichment, behavioral anomaly detection, brute force, the BEC kill chain, ransomware patterns, posture scoring, and more.
-
Full catalog: see all 36
Detailed description, severity scoring, and example alert for every engine.
See every engine
Compliance mapped
Every control mapped to the frameworks your customers and auditors ask about.
Pro subscribers get the Cyber Insurance Evidence Report — a 7-page audit-ready PDF generated from your real monitoring data, quarterly.
- ABA Model Rule 1.6
- IRS Publication 4557
- FTC Safeguards
- SEC Reg S-P
- NAIC Model Law 668
- CMMC 2.0
- GLBA
- NIST 800-171
- NY DFS 23 NYCRR 500
- State breach notification
Connect once. Monitored around the clock. Under 10 minutes.
Cancel in one click from the dashboard.